Every organisation depends on information assets to support its daily operations. Business applications, databases, cloud services and critical documents all contribute to business performance. However, without clear ownership and structured management, these resources can introduce security risks and operational challenges. Effective asset management strategies help organisations understand which resources matter most, assess potential threats and maintain appropriate controls.
By connecting asset information with risk management and compliance processes, businesses can make more informed decisions and improve operational resilience. This article explores practical strategies for managing information assets, reducing operational risks and supporting regulatory compliance.
Why Asset Management Matters for Risk Reduction
Poor asset visibility creates problems across multiple departments. For example, an organisation may rely on a critical application without knowing which business processes depend on it. If that application becomes unavailable, teams may struggle to understand the potential consequences. Similarly, unclear ownership can delay risk assessments and security decisions.
A structured asset management approach helps organisations address these challenges by maintaining accurate information about important resources. Furthermore, it creates a foundation for identifying vulnerabilities, evaluating operational risks and documenting appropriate measures.
Five Asset Management Strategies That Improve Security and Compliance
Build and Maintain an Information Asset Register
The first step is to identify the information assets that support business operations. An asset register should include relevant applications, databases, information systems, cloud services and other important resources. For each asset, organisations should document its purpose, responsible owner and business importance.
However, creating an inventory is only the beginning. Teams must also review records regularly to reflect changes in systems, suppliers and business activities. Accurate information helps organisations identify critical resources and prioritise management activities.
Classify Assets and Assign Clear Responsibilities
Not every information asset requires the same level of attention. A critical customer database may have a significantly greater business impact than an internal testing application. Therefore, organisations should classify assets according to their importance, sensitivity and operational role. In addition, each important asset should have a clearly identified owner.
Asset owners help maintain relevant information, participate in risk assessments and support decisions about appropriate protection measures. Clear responsibilities also improve coordination between IT, information security, compliance and business management teams.
Identify Dependencies and Assess Operational Risks
Information assets rarely operate independently. A business application may depend on a database, external cloud provider or authentication service. Disruption to one component can therefore affect several business processes. Documenting these relationships helps organisations understand potential operational consequences and can support a Business Impact Analysis (BIA) .
Next, teams should assess relevant risks by considering their likelihood and potential business impact. For example, an unavailable cloud service could interrupt customer orders or prevent employees from accessing essential information. A structured risk analysis helps management determine which risks require additional controls and which can be accepted within defined limits.
Implement Security Controls and Risk Treatment Measures
Identifying risks is not enough. Organisations must also determine how to manage them. Depending on the risk, appropriate measures may include access restrictions, employee training, backup procedures, supplier requirements or improvements to business processes. For example, access to sensitive information should reflect employees’ responsibilities and legitimate business needs.
Organisations should also document risk treatment decisions, assign action owners and establish appropriate review dates. After implementing measures, teams need to reassess the remaining risk. This approach connects risk analysis with practical security improvements.
Review Asset Records and Security Measures Regularly
Asset management is an ongoing process rather than a one-time project. New systems, organisational changes and external suppliers can introduce additional risks. Consequently, previously completed assessments may become outdated. Regular reviews help teams verify ownership, confirm dependencies and evaluate whether existing controls remain appropriate.
Management should also receive relevant information about significant risks and unresolved actions. By maintaining consistent review practices, organisations can respond more effectively to changes in their operating environment.
How Asset Management Supports Regulatory Compliance
Information asset management plays an important role in information security governance. ISO/IEC 27001 provides a risk-based framework for establishing and maintaining an information security management system. Annex A control 5.9 addresses inventories of information and other associated assets.
The NIS2 Directive , particularly Article 21 , establishes cybersecurity risk management requirements for organisations within its scope. In Slovenia, the Information Security Act (ZInfV-1) establishes national obligations for covered entities. Article 21 of ZInfV-1 addresses requirements including relevant asset inventories, risk analysis and security documentation. Article 22 addresses technical, operational and organisational security measures.
However, these requirements do not automatically apply to every business. Organisations must determine their regulatory obligations based on their activities and legal classification. Asset management software can support documentation and oversight, but it does not establish compliance without appropriate organisational measures.
Practical Example: Reducing Risk in a Critical Business Process
Consider a company that manages customer orders through a cloud-based application. Several departments rely on the application, while an external provider hosts its supporting infrastructure. First, the organisation records the application and identifies its responsible owner. Next, the team documents its dependencies and determines which business processes could be affected by an interruption. A risk assessment then evaluates potential threats and their business impact.
Based on the findings, management may introduce alternative operating procedures, review provider arrangements or improve recovery documentation. Finally, responsible employees monitor the implementation of these measures and review the remaining risk. This example shows how asset management supports practical risk reduction without requiring automatic infrastructure monitoring.
Measuring the Business Value of Asset Management
Organisations should evaluate whether their management activities produce useful results. Rather than assuming guaranteed financial savings, teams can measure improvements through relevant operational indicators.
Examples include:
- Percentage of critical assets with assigned owners
- Completeness and accuracy of asset records
- Number of overdue risk treatment actions
- Time required to prepare information for internal reviews
- Percentage of critical dependencies documented
- Completion of scheduled risk and asset reviews
These indicators help management identify weaknesses and evaluate progress. Over time, more reliable asset information can also support better planning, clearer accountability and more consistent business decisions.
Asset Management Strategies Checklist
Use this checklist to review how your organisation manages information assets, responsibilities, operational risks and security measures.
This checklist is a practical management aid. Completing it does not establish compliance with NIS2, ZInfV-1 or ISO/IEC 27001. Organisations must assess applicable requirements, implement appropriate measures and maintain supporting evidence separately.
Frequently asked questions
Important strategies include maintaining an accurate asset register, assigning ownership, classifying criticality, documenting dependencies and conducting regular risk assessments.
It helps organisations identify important resources, understand potential disruptions and prioritise appropriate mitigation measures.
Yes. Software can help maintain structured asset records, risk assessments and supporting documentation. However, organisations must still implement applicable requirements and demonstrate that their controls are effective.
Yes. Smaller organisations can benefit from clear asset ownership and consistent risk management. The level of detail should reflect their size, complexity and business needs.
How Blue Octopus Supports Asset Management and Risk Reduction
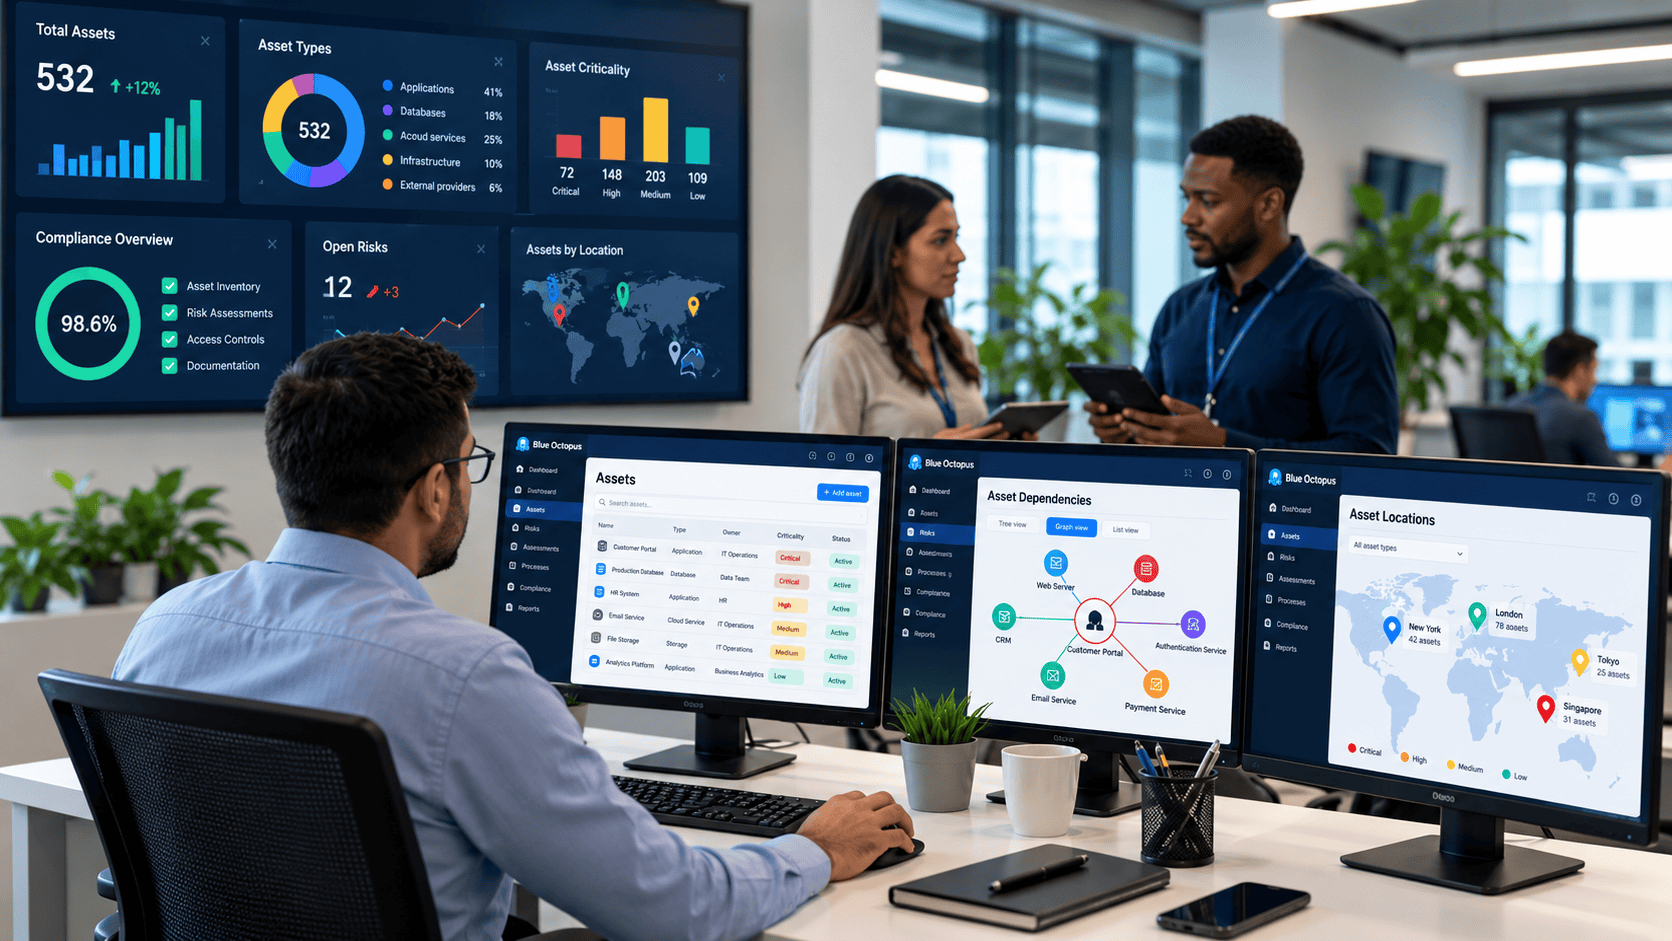
Blue Octopus helps organisations structure information asset management, risk assessments and supporting documentation. The platform provides configurable asset registers where teams can document important business resources, assign ownership and classify criticality. Additionally, visual dependency mapping helps organisations understand relationships between information assets.
Structured risk assessments enable teams to evaluate likelihood and impact, document mitigating measures and review residual risks. Blue Octopus also supports business process management, Business Impact Analysis and compliance documentation. Together, these capabilities help organisations connect asset information with operational risks, responsibilities and relevant requirements.
However, Blue Octopus does not replace specialised vulnerability scanners, automatic device discovery, predictive maintenance or technical security controls. Explore the Blue Octopus modules for more information about the available functionality.
Build a Stronger Foundation for Security and Performance
Effective asset management strategies connect business resources with responsibilities, operational risks and security measures. By maintaining accurate asset records, understanding dependencies and reviewing risks regularly, organisations can improve decision-making and support more consistent compliance practices.
The goal is not simply to collect information. It is to use that information to protect critical operations and guide practical improvements. Discover Blue Octopus to learn how structured information asset management and risk analysis can support your organisation.
