


Software risk analysis helps organisations identify weaknesses that could disrupt the applications and systems they rely on. By reviewing software alongside its owners, information assets and business processes, teams can see where technical problems may create wider operational risks.
A structured assessment considers the likelihood and impact of potential failures, the safeguards already in place and the actions needed to reduce exposure. It also helps teams agree on priorities and revisit risks when systems change. For practical guidance on risk assessment, see the NIST Guide for Conducting Risk Assessments.
When software risk analysis forms part of asset management, decisions are supported by clearer records and defined responsibilities. This approach can improve preparedness without suggesting that every incident can be prevented.
Enhancing Asset Monitoring in Real Time
Up-to-date asset information helps teams understand which software and services support daily operations. Monitoring tools may reveal performance changes, unusual activity or service interruptions, while an asset register provides the context needed to interpret those signals.
For example, a warning about a shared database becomes more useful when teams know which applications depend on it. They can assess affected processes, involve the responsible owners and decide which issue requires attention first.
Monitoring does not replace software risk analysis. Combining operational observations with documented dependencies and periodic risk reviews gives organisations a better basis for responding to change.
Key Areas for Integrating Software Risk Analysis
Identify Software and Resource Dependencies
Start with an inventory of important applications, the information they process and the business services they support. Record owners and dependencies on databases, infrastructure and external providers.
This context helps teams understand where one software issue could affect several operations. Review the information when systems, responsibilities or suppliers change.
Assess Potential System Failures
Consider how software vulnerabilities, configuration errors or unavailable services might interrupt important processes. Evaluate likelihood and impact using criteria that are consistent across the organisation.
Document existing safeguards and identify risks that require further treatment. Risk analysis helps prioritise prevention and recovery, but cannot guarantee that failures will never occur.
Plan Responses and Assign Owners
For each material risk, agree on an appropriate response and assign a responsible owner. Actions may include software updates, configuration reviews, access changes or recovery tests, depending on the findings.
Keep the decision, priority and follow-up action connected to the relevant asset record. This makes it easier to review progress and explain why a particular measure was selected.
Protect Access and Sensitive Information
Software risk reviews should consider who can access important systems and what information those systems hold. Access permissions, authentication and data protection measures should reflect the actual risks.
Document relevant controls and check whether they remain effective as applications and users change. An asset management record supports oversight but does not itself enforce technical security measures.
Use Evidence to Review Priorities
Incident records, testing results and system changes provide useful evidence for reviewing software risks. Compare new information with earlier assessments to see whether likelihood, impact or safeguards have changed.
Update the risk register and communicate significant changes to the people responsible for affected services. A regular review keeps risk decisions relevant to current business priorities.
Improve Workflows Without Assuming Automation
Clear ownership, consistent records and agreed review cycles can reduce duplicated administrative work. Teams can use software tools to organise information and follow-up activities more effectively.
Automation may help where suitable tools and processes exist, but it is not a substitute for assessing risks or making accountable decisions. Keep the emphasis on reliable information and practical actions.
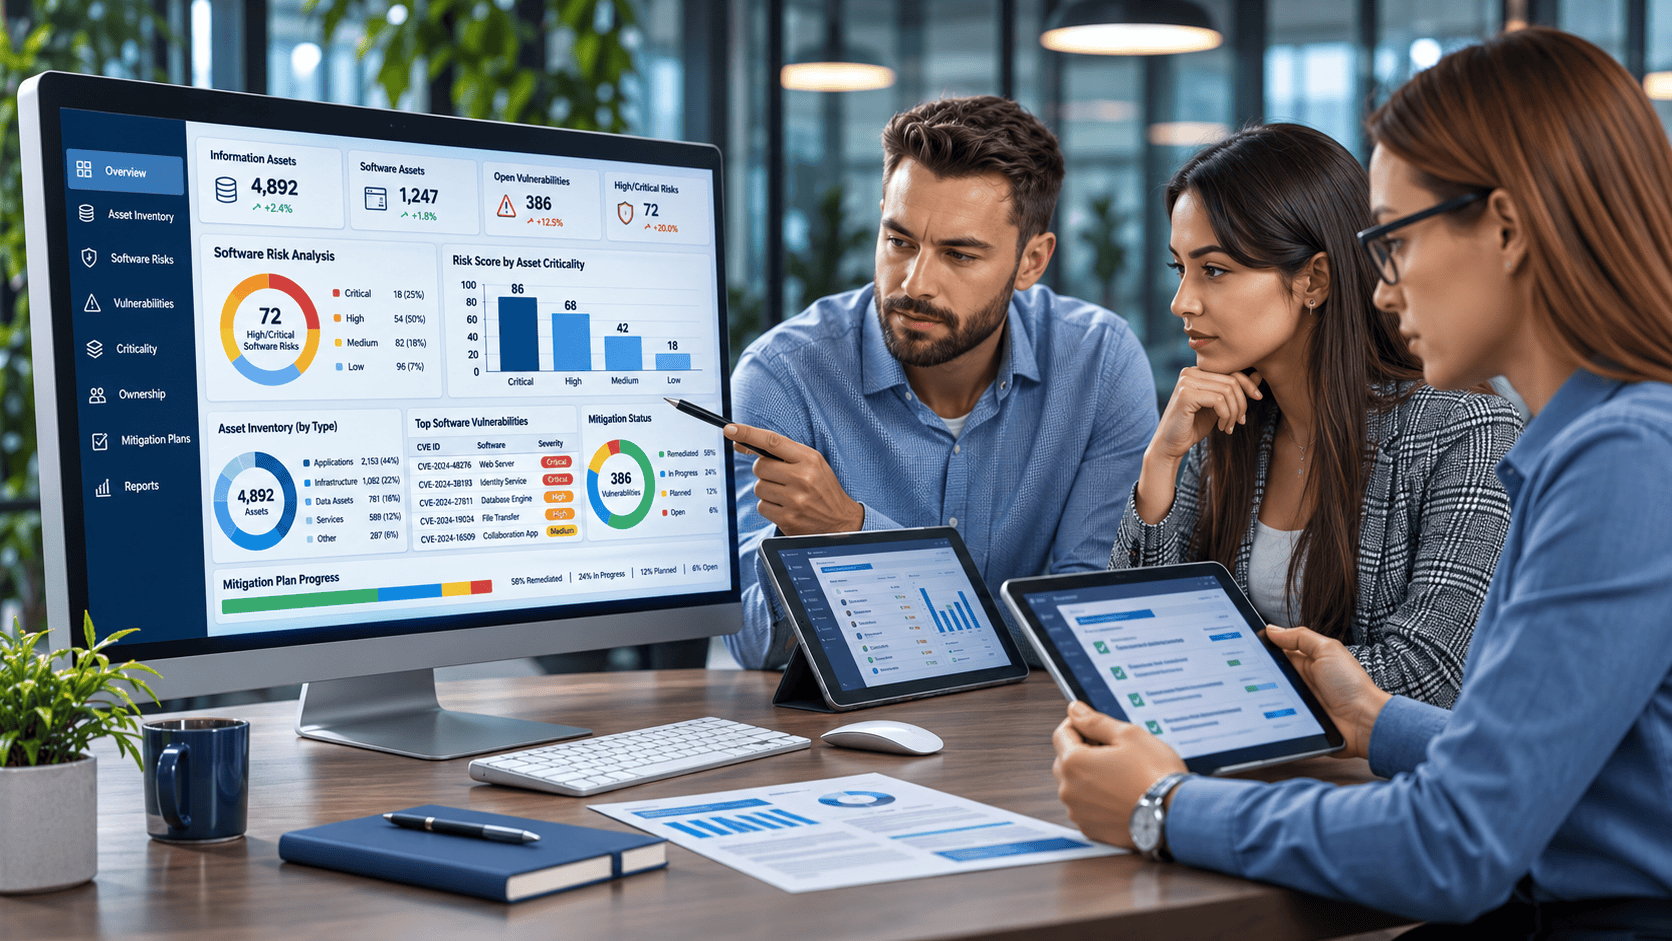
Practical Example: Addressing a Software Dependency Risk
Consider an organisation that uses an important business application connected to several shared information assets. A routine review reveals that the application depends on an ageing software component and that disruption could affect multiple teams. The organisation records the affected application, its owner and relevant dependencies before assessing how a failure could interrupt its processes.
The team then evaluates the likelihood and potential impact of the risk, identifies existing safeguards and agrees on a proportionate response. Possible actions could include updating the component, testing recovery procedures or assigning additional review responsibilities. These are illustrative risk-management decisions, not actions automatically performed by a particular platform.
By revisiting the assessment when assets or business requirements change, the organisation can keep the technical risk connected to operational priorities. The example shows how software risk analysis can become part of regular asset management rather than a disconnected one-time exercise.
Software Risk Analysis and Asset Management Checklist
Use this practical checklist to review how software risks are considered alongside information assets, their owners and business dependencies.
This checklist is a practical review aid, not proof that all software or regulatory risks have been addressed.
How Blue Octopus Can Help
Blue Octopus brings information assets, their owners and dependencies into a shared management environment. Its asset management modules support customisable asset records, criticality classification and a visual view of connections, giving teams a more structured basis for identifying what a software issue might affect.
The platform also supports risk analysis for individual assets, with likelihood and severity assessments, initial and residual risk evaluation, and mitigation measures. Teams can connect these assessments with relevant processes and use the resulting records to support structured review and decision-making.
For organisations integrating software risk analysis into asset management, this approach helps bring asset context, business impact and risk responsibilities into one workflow. Blue Octopus supports the documentation and assessment process; it does not by itself guarantee the prevention of technical failures or legal compliance.
Connecting Software Risks with Asset Management
Software risk analysis is most useful when it reflects how an organisation actually operates. An assessment should explain which asset is affected, which processes depend on it and who is responsible for reviewing the risk.
A connected asset register helps teams keep this context alongside the risk assessment and proposed actions. When software, suppliers or business priorities change, they can review the affected relationships instead of starting from isolated documents.
The goal is not to eliminate every technical risk, but to recognise important dependencies, make informed decisions and keep the necessary actions visible.
Frequently Asked Questions
It is a structured process for identifying, assessing and treating risks that may affect software, the services it supports and related information assets.
It helps teams prioritise weaknesses, plan proportionate measures and understand the business impact of potential failures.
It connects software-related risks with asset records, owners and dependencies, giving teams clearer information for decisions and follow-up.
Accurate information about assets, incidents and system changes helps teams reassess risks and identify problems that need attention.
They can organise records, responsibilities and planned measures in one place. Their value depends on the quality of the assessments and actions taken.